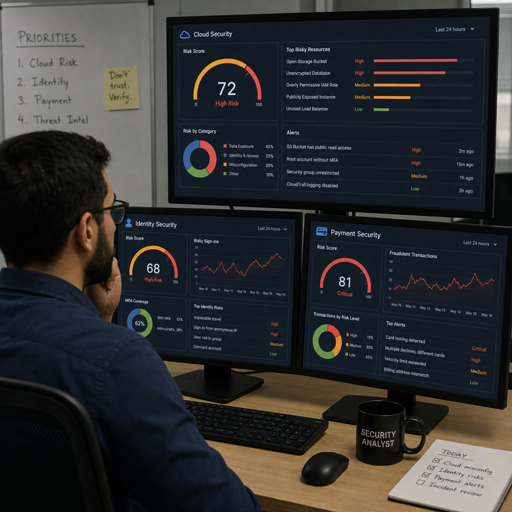
Cybersecurity in 2026 is being shaped by faster attackers, wider AI adoption, more complex cloud environments, and a payments ecosystem where fraud is increasingly social, automated, and identity-driven. The most important Cybersecurity trends 2026 leaders should watch are not just new tools, but new operating habits: stronger identity controls, better visibility, secure AI use, resilient payment flows, and practical preparation for post-quantum cryptography.
Which cybersecurity trends matter most in 2026?
The trends that matter most are the ones changing everyday risk: AI-assisted attacks, identity abuse, vulnerability exploitation, ransomware pressure, cloud and API exposure, payment fraud, MSP risk, and early post-quantum planning. Gartner’s 2026 cybersecurity outlook grouped major priorities around securing new frontiers, transforming governance, and normalizing AI adoption, while its February 2026 trend coverage pointed to AI disruption, geopolitical tension, regulatory volatility, and an accelerating threat landscape as key forces behind security strategy.
For business leaders, that means cybersecurity can no longer sit at the edge of IT. It has to be part of product design, customer experience, vendor selection, payment operations, and employee behavior. The organizations that do best in 2026 will not be the ones chasing every new security technology trend; they will be the ones reducing attack paths before incidents begin.
Key takeaways for security teams
Use these priorities as a practical starting point when reviewing your roadmap:
- Treat identity as the new perimeter. Focus on phishing-resistant authentication, privileged access, machine identities, and continuous access review.
- Govern AI before it governs you. Create clear rules for approved AI tools, sensitive data handling, model access, and employee use.
- Patch based on exploitability, not just severity. Vulnerability exploitation has become a more visible breach entry point, so prioritization matters.
- Modernize payment security. Tokenization, passkeys, behavioral signals, and AI fraud detection are becoming more central to digital payments.
- Expect ransomware to combine tactics. Attackers increasingly blend stolen credentials, social engineering, exposed systems, and extortion.
- Start post-quantum discovery now. Migration will take time, especially for certificates, embedded systems, third-party dependencies, and long-lived data.
AI is becoming both the attack surface and the defense layer
AI is no longer a side topic in security planning. Attackers can use generative tools to write more convincing phishing messages, automate reconnaissance, support malware development, and scale social engineering. A 2026 survey of AI-driven cybersecurity risks described deepfakes, synthetic media, adversarial AI, automated malware, and AI-powered social engineering as major emerging threat categories.
At the same time, defenders are using AI for alert triage, fraud scoring, anomaly detection, code analysis, and faster investigation. The problem is not AI itself; it is unmanaged AI. If employees paste sensitive data into public tools, if teams deploy AI agents without access controls, or if models connect to critical systems without monitoring, the organization creates new risk faster than security can measure it.
A practical 2026 AI security program should include an inventory of AI tools, policies for data classification, logging for model and agent activity, red-team testing for high-risk use cases, and approval paths for AI connected to production systems. The goal is not to block innovation. It is to make AI adoption observable, governed, and secure enough to scale.
Identity security is moving beyond passwords
Identity remains one of the most valuable targets because it gives attackers a legitimate-looking path into systems. The 2026 Verizon DBIR highlighted human factors such as social engineering, phishing, stolen credentials, vulnerability exploitation, and ransomware as continuing drivers of breaches, and Verizon’s 2026 coverage also noted growth in shadow AI and mobile social engineering risks.
In 2026, security teams should move beyond basic multi-factor authentication and toward phishing-resistant controls where possible. Passkeys, hardware security keys, device binding, conditional access, and risk-based step-up authentication can reduce exposure to credential theft and MFA fatigue. This is especially important for administrators, finance users, developers, executives, and anyone with access to sensitive customer or payment data.
Machine identities also deserve more attention. Service accounts, API keys, tokens, bots, and AI agents often have broad access and weak lifecycle controls. If these identities are not inventoried, rotated, monitored, and limited, they become quiet paths for escalation.
Payment security is shifting from card protection to trust protection
The top emerging cybersecurity trends in digital payments 2025 2026 revolve around trust: proving who is paying, whether the transaction is legitimate, and whether the device, account, or AI agent involved should be allowed to act. Visa’s Spring 2026 Biannual Threats Report said scams had become the fastest-growing source of consumer harm as criminals increasingly used AI and social engineering to convince people to authorize payments themselves.
This shift matters because many older fraud models were designed to stop stolen-card misuse, not to detect a real customer being manipulated in real time. That is why modern payment defense is leaning into tokenization, behavioral analytics, device intelligence, biometric authentication, passkeys, and network-level risk scoring.
Businesses researching stripe cybersecurity trends in payments 2025 2026 will notice a similar theme: fraud tools are expanding beyond card transactions. Stripe announced in May 2026 that Radar had expanded to protect supported payment volume globally across bank debits, BNPL, crypto, digital wallets, real-time payments, and cash vouchers, with businesses able to pass additional structured risk signals into Stripe.
Searches around visa inc cybersecurity trends in payments 2025 2026 also point to tokenization, AI-enabled fraud defense, payment passkeys, and safer digital commerce. Visa has described tokenization as replacing sensitive payment details with unique values to help reduce fraud and improve customer experience, and its 2025 payments outlook emphasized AI-powered fraud prevention and biometric authentication through products such as Visa Payment Passkey.
What changed around cybersecurity trends February 2026?
Cybersecurity trends February 2026 became a useful marker because several major outlooks around that period emphasized the same reality: AI, identity, governance, and emerging infrastructure risk were converging. Gartner’s February 5, 2026 announcement specifically tied its top trends to AI’s rapid rise, geopolitical tensions, regulatory volatility, and a faster-moving threat landscape.
For practitioners, that timing matters less than the strategic signal. Security programs can no longer rely on annual control reviews and slow policy updates. New AI tools, SaaS integrations, vendor connections, and payment methods can enter the business quickly, often before formal risk assessment catches up.
The practical response is to shorten feedback loops. Review access more often. Monitor new cloud services and AI tools automatically. Build security checkpoints into procurement and product development. Replace static awareness training with behavior-focused coaching for phishing, payment fraud, data handling, and AI use.
MSP cybersecurity trends 2026 are centered on trust and accountability
MSPs are under pressure because they sit close to client infrastructure, credentials, backups, endpoints, and cloud systems. That makes them valuable partners and attractive targets. ConnectWise’s 2026 MSP Threat Report described a shift in attacker strategy toward identity, access, and trust relationships, noting that adversaries were not relying primarily on novel exploits.
For MSPs and their customers, this changes the conversation. It is not enough to ask whether an MSP offers monitoring or endpoint protection. Customers should ask how privileged access is controlled, how technician activity is logged, how backups are isolated, how incidents are escalated, and how the MSP secures its own tooling.
A strong MSP security model in 2026 should include:
- Separate administrative accounts for customer environments, with least privilege and strong authentication.
- Documented incident response roles so the MSP and client know who acts first during ransomware, fraud, or account compromise.
- Backup resilience testing rather than assuming backups will restore when needed.
- Toolchain hardening for remote monitoring, ticketing, scripting, and automation platforms.
- Transparent reporting on patch status, endpoint coverage, detected threats, and unresolved risks.
Ransomware is becoming more operational than purely technical
Ransomware in 2026 is less about a single malicious file and more about business disruption. Attackers may exploit exposed systems, buy stolen credentials, phish employees, compromise vendors, steal data, and threaten disclosure. CISA’s ransomware guidance has continued to emphasize cloud backups, zero trust architecture, and practical steps such as reducing maintenance burdens for identity and email systems where appropriate.
The defensive focus should be resilience. Organizations need to know which systems are most critical, how quickly they can restore them, which dependencies could block recovery, and who can approve emergency decisions. A tabletop exercise often reveals gaps that tools cannot: unclear authority, missing vendor contacts, untested backups, or payment systems that cannot operate manually.
Ransomware preparation should include immutable or isolated backups, tested restoration, endpoint detection, network segmentation, privileged access controls, and clear communication plans. Just as important, teams should practice decision-making before the pressure of an active incident.
Cloud, SaaS, and API security are becoming everyday security work
Cloud risk is no longer limited to misconfigured storage buckets. Modern environments include SaaS platforms, identity providers, CI/CD pipelines, serverless functions, data warehouses, APIs, third-party integrations, and AI services. Google Cloud’s H1 2026 threat reporting described incidents involving LLM-assisted credential harvesting, cloud administration access, identity-based controls, API log correlation, and ransomware or extortion activity affecting cloud resources.
This makes visibility essential. Security teams need to know which identities can access which data, which APIs are exposed, which secrets exist in repositories, and which workloads can communicate with each other. Without that context, cloud alerts become noise.
A practical cloud security plan should prioritize asset inventory, identity governance, secrets management, logging, runtime monitoring, data loss controls, and configuration baselines. If your team cannot answer “what changed?” after a suspicious event, detection and response will be slower than the attacker.
Post-quantum cryptography is becoming a planning requirement
Post-quantum cryptography may feel distant, but 2026 is a sensible year to begin serious discovery. NIST released its first three finalized post-quantum cryptography standards in 2024, and its migration guidance stresses the need to identify quantum-vulnerable public-key algorithms in hardware, software, and services before building a roadmap.
The immediate task is not to replace every cryptographic system overnight. It is to understand where cryptography lives: TLS certificates, VPNs, code signing, firmware updates, customer data stores, payment systems, vendor products, and long-retention archives. Organizations with sensitive data that must remain confidential for years should pay particular attention to “harvest now, decrypt later” risk.
Security leaders should work with infrastructure, application, compliance, and procurement teams to build crypto inventories and require vendors to explain their post-quantum roadmaps. Crypto-agility—the ability to change algorithms without redesigning entire systems—will become a valuable resilience capability.
Security technology trends are becoming more integrated
The most useful security technology trends in 2026 are not isolated point products. They are integrated capabilities that help teams see risk, make decisions, and act faster. Examples include identity threat detection and response, exposure management, attack surface management, cloud-native application protection, data security posture management, software supply chain controls, and AI-assisted SOC workflows.
However, more tooling does not automatically mean better security. Many teams already have more alerts than they can handle. The better question is whether a tool reduces time to detect, time to contain, or time to recover. If it does not improve one of those outcomes, it may add cost and complexity without reducing risk.
When evaluating new technology, ask:
- What risk does this reduce that we cannot already manage?
- What data sources does it need to work well?
- Who will own the alerts, tuning, and response process?
- Does it integrate with identity, ticketing, cloud, endpoint, and SIEM workflows?
- How will we measure value after 90 days?
A practical 2026 cybersecurity checklist
Use this checklist to turn trend-watching into action:
- Inventory critical assets, identities, APIs, SaaS tools, AI tools, and payment systems.
- Move high-risk users to phishing-resistant authentication.
- Review privileged access for employees, vendors, service accounts, and MSPs.
- Prioritize vulnerabilities based on exploitation, exposure, and business impact.
- Test backup restoration for critical systems, not just backup completion.
- Document payment fraud escalation paths for finance, support, and operations teams.
- Create approved AI use policies and monitor for unapproved tools.
- Ask key vendors about breach notification, logging, security controls, and post-quantum plans.
- Run at least one incident tabletop focused on ransomware, payment fraud, or cloud compromise.
- Report security progress in business terms: reduced exposure, faster response, and improved resilience.
The organizations that win will simplify risk
Cybersecurity trends 2026 can feel overwhelming because every topic seems urgent. AI is accelerating attacks and defense. Payments are becoming more digital and more identity-dependent. MSPs are being judged on trust. Cloud environments are expanding. Quantum-safe migration is entering the planning cycle.
The way forward is to simplify the mission: protect identities, reduce exposed systems, govern AI, secure payment journeys, test recovery, and build visibility across the environments that matter most. Organizations that focus on these fundamentals will be better prepared for both the threats they can predict and the surprises they cannot.