Researchers studying AI provenance say some image watermarks can remain detectable even after watermarked images are used to train a new generative model, but the result depends strongly on the watermarking method and the model architecture. The finding adds a new dimension to image watermarking research, shifting attention from whether a mark survives cropping, compression, or editing to whether it survives the next training cycle. The work is especially relevant as synthetic images spread online and may be scraped back into future training datasets.
What did the researchers find?
The researchers found that AI image watermark durability is not a single property that applies equally across watermark systems. In tests reported by CISPA Helmholtz Center for Information Security researchers, some watermark signals degraded after one training-and-generation cycle, while another remained detectable across later generations, including when only a small share of the training set was marked. CISPA’s summary says the study used a dataset inference framework that aggregates weak per-sample signals through statistical hypothesis testing, allowing detection even when individual traces are subtle.
The paper, “Watermark Degradation Across Model Iterations,” was published on June 17, 2026, and presented at the ACM Workshop on Information Hiding and Multimedia Security, known as IH&MMSec ’26. Its authors are Michel Meintz, Maitri Vignesh Shah, Bihe Zhao, Louis Kerner, Franziska Boenisch, and Adam Dziedzic. TechXplore reported on the work on October 9, 2026, highlighting the practical question the team set out to answer: whether a watermark can still help prove that a new model was trained on marked synthetic data.
The answer, based on the study, is cautiously yes. Watermarks may survive retraining, but not reliably enough to treat all current systems as interchangeable image security techniques. The design of the watermark and the generation method used by the model both matter, which means AI image protection strategies may need to be tailored to specific model families rather than deployed as universal labels.
The study tested watermarks through a second model
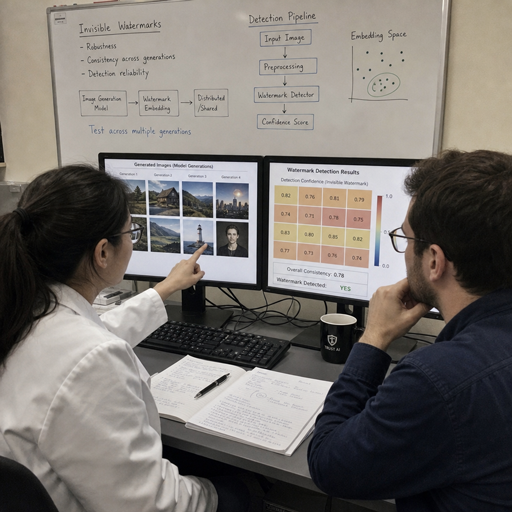
The experiment followed a two-stage process. First, the researchers used a model to generate images carrying watermarks. Then they used those AI-generated images as training data for a second generative model and examined whether images created by that second model still carried a detectable signal.
That setup reflects an increasingly important real-world problem. AI-generated images do not remain isolated after publication. They are posted, copied, compressed, reposted, and potentially scraped into datasets for later model training. If a watermark disappears during that process, it may still help identify a single generated image, but it becomes less useful for tracing whether synthetic material entered a later model’s training pipeline.
The team evaluated four watermarking methods: TrustMark, StableSignature, TreeRing, and BitMark. They also tested across two broad model architectures: diffusion models and autoregressive image models. Rather than relying only on one image at a time, the researchers analyzed watermark signals statistically across datasets, an approach that can reveal weak patterns that may not be obvious in individual outputs.
Why watermark durability matters now
The durability question is becoming more urgent because synthetic content can create feedback loops. If companies or researchers unknowingly train new systems on large volumes of AI-generated imagery, they may reduce data quality or reinforce artifacts and biases already present in previous generations of models. CISPA’s publication summary notes that training on generated data has been shown to degrade model performance and amplify existing biases, making data provenance more than a compliance concern.
Watermarking offers one possible safeguard. Invisible watermarks can embed signals into image data so a detector can later identify generated content or trace its origin. Google DeepMind has described SynthID as a tool that embeds digital watermarks directly into AI-generated media, while noting that traditional visible watermarks can be edited out more easily.
That distinction is central to current image protection debates. A visible logo or label may inform viewers, but it can be cropped, blurred, or copied without context. More robust image watermarking aims to place the signal inside the data itself, making it harder to remove through ordinary file handling. Even so, robustness against everyday transformations is not the same as robustness against model retraining, where the signal must influence what a new model learns.
BitMark stood out, but the result was architecture-specific
Among the tested approaches, BitMark performed particularly well in the reported experiments. TechXplore’s account of the study says BitMark, developed by SprintML, remained reliably detectable in the Infinity-2B model even when only 1% of the training data was marked. CISPA’s publication summary similarly notes that one method stayed highly detectable in subsequent generations at the 1% marked-data level, while other watermarks degraded severely and had a finite lifetime.
That result is significant, but it should not be read as a blanket endorsement that one watermark solves the problem for all AI image protection use cases. The researchers emphasized that transferability depends heavily on model structure. A watermark that survives well in one setting may not behave the same way in a diffusion model, an autoregressive model, or a future architecture that uses a different representation of images.
The practical implication is that watermarking systems may need to be evaluated in the same conditions where they are expected to operate. For content platforms, model developers, publishers, and rights holders, that means asking not only “Can this detector find the mark today?” but also “Can the signal persist after the content becomes training data?”
Key details from the research
- Research focus: whether watermarks in AI-generated images remain detectable after those images are used to train another generative model.
- Methods tested: TrustMark, StableSignature, TreeRing, and BitMark.
- Architectures tested: diffusion models and autoregressive image models.
- Detection approach: statistical analysis across datasets, rather than relying only on single-image detection.
- Main finding: watermark persistence varies widely by design and architecture; some signals degrade quickly, while BitMark showed strong durability in the tested Infinity-2B setting.
- Open challenge: building watermarking methods that are durable across retraining, practical across providers, and strong enough for more granular detection.
Standardization remains a major obstacle
The study also points to a coordination problem. If each AI provider uses a different watermark, one company may be able to detect its own marks but miss synthetic images produced by another provider. Meintz told TechXplore that a common watermark recognized across providers could simplify synthetic-data filtering, but he also noted that agreement may be difficult because companies have different requirements and watermark structures continue to evolve.
That challenge affects both governance and engineering. Regulators, platforms, and AI labs may want a consistent way to identify synthetic media, yet watermark design involves trade-offs among image quality, detection accuracy, secrecy, resistance to removal, and compatibility with different generation systems. A common scheme could improve interoperability, but it could also create a larger target for attackers if detection methods or embedding patterns become widely understood.
For now, the study suggests that watermarking should be treated as one layer in a broader provenance system. Metadata, content credentials, platform labeling, dataset documentation, and model-level safeguards can support one another. Invisible image watermarking may be especially useful when metadata is stripped, but it cannot answer every provenance question alone.
The next research goal is stronger single-image detection
The CISPA team’s current process requires analysis across a dataset to determine whether watermark traces are present. Meintz said the longer-term goal is to detect from a single image whether it was generated by a model trained on watermarked data. Achieving that would require a significantly stronger watermark signal, and he plans to build further on the principles behind BitMark while extending them beyond the Infinity architecture.
That next step could make AI image security techniques more practical for investigators, platforms, and dataset curators. Dataset-level inference can be useful for audits, but single-image detection would be more actionable in moderation workflows, rights management, and public-facing provenance tools. It would also raise new design questions about how to strengthen a signal without creating visible artifacts or making removal easier.
The broader message from the research is measured rather than absolute. Watermarks are not doomed to disappear when AI-generated images enter new training cycles. But durability varies, and reliable AI image watermark durability will require watermark designs built specifically for the realities of generative model retraining.