Frontier AI is moving from a research story to a boardroom, policy, and public trust story. As the most capable models become more powerful, some of the same industry giants funding AI innovation are also arguing for a slower, more controlled path for frontier AI development. This article explains why that tension exists, what it means for AI research trends, and how teams can keep building responsibly without treating speed as the only measure of progress.
Why are industry giants calling for a slower pace in frontier AI?
Industry giants are pushing to slow down frontier AI because the stakes are no longer limited to model performance, product demos, or competitive advantage. Frontier AI systems can influence software creation, cybersecurity workflows, scientific research, media production, education, and decision-making at scale, so mistakes can spread faster and affect more people. A slower pace does not necessarily mean stopping AI breakthroughs; it often means adding stronger safety testing, governance, infrastructure controls, and clearer accountability before the most powerful systems are widely released.
This creates a complicated moment for the AI sector. The companies with the most resources are often the ones best positioned to build frontier tech, yet they are also the ones most exposed to public scrutiny, regulatory pressure, and reputational risk. When a large lab or platform company argues for caution, it may be motivated by genuine safety concerns, competitive strategy, operational limits, or all of those at once.
For readers trying to understand the debate, the key point is simple: the conversation is not “innovation versus fear.” It is about whether AI development should be paced by what can be built, what can be safely deployed, or what society is ready to absorb.
Frontier AI has changed the meaning of responsible speed
In earlier waves of software, shipping fast was often treated as a virtue. A product team could release, watch user behavior, patch bugs, and improve. That model becomes harder to defend when systems can generate code, synthesize persuasive content, automate workflows, or interact with sensitive information in ways even their creators may not fully predict.
Frontier AI raises the bar because capability is not always visible from a standard product demo. A model may appear useful in ordinary tasks while also creating new risks in edge cases, adversarial prompts, or high-stakes environments. Responsible speed therefore means more than moving slowly. It means moving with enough testing, documentation, and restraint to understand what is being released.
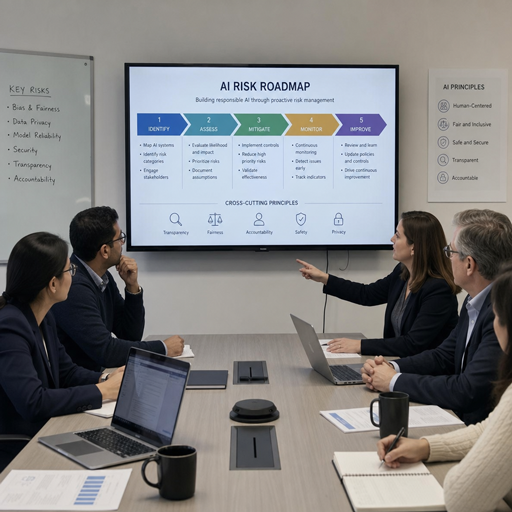
This shift is affecting AI research trends in practical ways. More attention is moving toward model evaluations, interpretability, red teaming, secure deployment, misuse monitoring, data governance, and post-release oversight. These areas may sound less glamorous than a new benchmark result, but they are becoming central to the next phase of AI innovation.
A mature frontier AI strategy treats safety work as part of the product, not a delay imposed after the product is finished. Teams that do this well can still move quickly, but they do not confuse velocity with readiness.
The business incentives behind the slowdown conversation
The push to slow down frontier AI is not driven by one motive. Large companies operate in a web of incentives: they want to lead the market, protect users, satisfy regulators, manage compute costs, recruit top researchers, and avoid catastrophic product failures. These incentives can pull in different directions.
On one hand, frontier labs AI teams want to produce AI breakthroughs that attract customers, partners, developers, and investors. Being first can matter when a new capability reshapes workflows or becomes a platform standard. On the other hand, being first with a poorly controlled system can create backlash, legal exposure, or long-term distrust.
There is also a strategic layer. Calls for caution can shape the competitive landscape. If only a few companies have the resources to meet strict safety, compute, and compliance expectations, slower development may favor incumbents over smaller challengers. That does not make caution wrong, but it does mean the public debate should be alert to who benefits from different rules.
A useful way to read industry statements is to separate the safety argument from the market effect. A proposal can be sincerely safety-minded and still reinforce the power of existing industry giants. A policy can reduce risk and still make it harder for new entrants to compete. The best governance conversations acknowledge both realities.
What does “slowing down” actually mean?
Slowing down frontier AI usually does not mean turning off research or abandoning AI development. It means adding gates between discovery, training, deployment, and widespread access so the strongest systems are evaluated before they are placed in the hands of millions of users or connected to critical workflows. The goal is not to block AI innovation, but to make the path from lab to market more deliberate.
In practice, a slower approach can include several different choices:
- Longer pre-release testing Models can be evaluated for harmful outputs, tool misuse, privacy weaknesses, security vulnerabilities, and behavior under pressure. This testing becomes more important when systems can act across tools or produce content at scale.
- Staged deployment Instead of releasing a powerful model broadly on day one, a company may begin with limited access, trusted partners, or controlled environments. This allows teams to learn from real-world use without exposing everyone to unresolved risks.
- Capability thresholds Organizations can define internal checkpoints for models that show certain levels of autonomy, persuasion, code generation, or domain-specific competence. When a system crosses a threshold, it receives additional review.
- Stronger monitoring after launch The work does not end at release. Teams need ways to detect misuse, unexpected behavior, prompt attacks, data leakage, and user harm after the system is live.
- Clearer governance and sign-off High-impact releases may need review by safety teams, legal teams, product leaders, security experts, and executives. This can slow decisions, but it also makes ownership clearer.
- Limits on certain use cases A model may be safe enough for drafting, summarizing, tutoring, or internal productivity, but not appropriate for fully automated decisions in healthcare, finance, hiring, law enforcement, or critical infrastructure.
The important distinction is between a thoughtful slowdown and vague caution. Thoughtful slowdown defines what must be tested, who decides, what evidence is needed, and what happens when a system fails a review. Vague caution simply says “be careful” without changing incentives or behavior.
The strongest arguments for caution
Supporters of a slower frontier AI path often begin with uncertainty. The most capable AI systems are not like conventional software, where every output can be mapped to a fixed rule. They can behave differently depending on prompts, context, tools, data, integrations, and user intent. That makes full prediction difficult.
Caution also comes from the scale of deployment. A single model can be integrated into search, office tools, developer environments, customer service systems, creative workflows, and enterprise platforms. If a weakness exists, it can show up across many industries at once.
The strongest case for slowing down includes several practical concerns:
- Misuse risk: Powerful models can help benign users work faster, but they may also lower the barrier for scams, misinformation, cyber abuse, or manipulation.
- Reliability gaps: Even advanced systems can produce incorrect, incomplete, or misleading outputs with confidence. In high-stakes settings, that can be dangerous.
- Concentration of power: If only a few frontier labs control the most capable systems, decisions about access, safety, and values may become too centralized.
- Infrastructure dependence: Businesses may build workflows around AI systems they do not understand or control, increasing operational fragility.
- Evaluation limits: A model may pass known tests while still failing in novel situations, especially when users creatively push its boundaries.
- Social adjustment: Schools, employers, creators, governments, and courts need time to adapt norms and rules around AI-generated work.
These concerns do not require panic. They require discipline. The best safety arguments are not anti-technology; they are pro-accountability.
The strongest arguments against slowing down too much
A slower approach can also create real costs. AI breakthroughs can help researchers analyze information, make software more accessible, support people with disabilities, improve productivity, and expand access to knowledge. Delaying useful systems may delay benefits as well as risks.
Critics of heavy slowdown efforts often worry that broad caution can become a tool for gatekeeping. If compliance requirements become too expensive or vague, smaller labs, open research groups, and startups may struggle to participate. That could reduce diversity in frontier tech and leave the future of AI development in the hands of a few large players.
There is also an international dimension. If one group of companies or countries slows down while others continue, safety-minded organizations may lose influence over the direction of the technology. In that scenario, the world may not get less frontier AI; it may simply get frontier AI developed by actors with different norms.
The anti-slowdown argument is strongest when it focuses on proportionality. Not every model, feature, or research project carries the same risk. A small tool that helps users organize notes should not face the same review burden as a highly capable system with autonomous tool use and broad deployment. Good governance should scale with actual risk.
A better frame is controlled acceleration
The most useful path may not be “speed up” or “slow down.” It may be controlled acceleration: moving quickly in areas where risks are understood and benefits are clear, while applying strict gates to systems with high capability, broad reach, or uncertain behavior.
Controlled acceleration recognizes that AI innovation needs momentum. Researchers need room to explore, developers need access to tools, and organizations need to learn by building. At the same time, it accepts that some releases should wait until teams can show evidence of safety, reliability, and operational readiness.
This approach also avoids treating all frontier AI work as equally dangerous. For example, research into better evaluation methods, privacy-preserving training, interpretability, secure deployment, and user controls may deserve more investment, not less. These areas can make future AI breakthroughs safer and more useful.
A practical controlled acceleration model might include:
- Fast lanes for low-risk research, internal tools, narrow productivity features, and safety-improving work.
- Review lanes for models that affect sensitive decisions, interact with external tools, or operate in regulated settings.
- Restricted lanes for systems that show advanced autonomy, high misuse potential, or unclear failure modes.
- Pause points when testing reveals serious weaknesses that cannot be mitigated before launch.
This gives teams a way to keep moving without pretending every release deserves the same level of trust.
Frontier labs are redefining competition
Competition in frontier AI used to be described mainly through model capability: who had the best benchmark, the largest model, the fastest inference, or the most impressive demo. Those signals still matter, but they are no longer enough. Increasingly, the leading organizations will be judged by how responsibly they manage capability.
That changes what it means to be a serious AI company. A lab that can produce impressive outputs but cannot explain its safety process may face skepticism from enterprises, policymakers, and the public. A company that can pair strong models with clear documentation, predictable controls, and careful deployment may earn deeper trust.
This is especially important for enterprise adoption. Businesses do not only want powerful systems; they want systems they can govern. They need to know how data is handled, how outputs should be reviewed, how errors are escalated, and what happens when a model behaves unexpectedly. Frontier labs AI programs that address these questions will be better positioned for durable adoption.
In this environment, safety becomes part of market differentiation. The next wave of AI research trends may reward organizations that can prove not only that their models are capable, but that their development process is mature.
What businesses should watch as AI development matures
Most organizations will not train frontier AI models themselves, but they will still be affected by the pace of frontier AI development. New capabilities will enter everyday software, cloud platforms, developer tools, analytics products, customer support systems, and creative workflows. That means business leaders need a way to evaluate AI beyond excitement.
A practical review process should include both opportunity and risk. Teams should ask where AI can reduce repetitive work, improve decision support, or unlock new services. They should also ask where errors, bias, security issues, or overreliance could create harm.
Before adopting a powerful AI system, organizations should consider:
- Use case fit: Is the model being used for drafting, analysis, decision support, automation, or direct decision-making?
- Human oversight: Who reviews outputs, and what authority do they have to override or reject them?
- Data exposure: What information is shared with the system, and how is sensitive data protected?
- Vendor transparency: Does the provider explain model limitations, safety practices, and update policies clearly?
- Failure planning: What happens if the system produces a harmful, false, biased, or insecure output?
- Change management: Are employees trained to use AI tools critically rather than blindly?
- Governance ownership: Which team is accountable for approval, monitoring, and escalation?
These questions are not meant to slow adoption for its own sake. They help organizations adopt AI in a way that survives contact with real operations. The businesses that benefit most from AI innovation will likely be those that build strong habits early.
The role of policy without freezing progress
Policy can help create shared expectations for frontier AI, especially when market incentives alone are not enough. However, policy works best when it is specific, adaptable, and focused on real risk. Broad rules that treat all AI systems the same can become outdated quickly or burden low-risk innovation unnecessarily.
A constructive policy approach may focus on transparency, testing, incident reporting, data protection, security, and accountability for high-impact deployments. It can also encourage collaboration between companies, researchers, civil society, and public institutions. The goal should be to create a floor for responsible behavior without locking the field into one technical path.
This matters because frontier tech evolves quickly. Rules that are too rigid may fail as model architectures, deployment methods, and use cases change. Rules that are too vague may be easy to praise and hard to enforce. The best frameworks leave room for learning while making clear that powerful systems require serious responsibility.
Policy should also avoid assuming that only the largest companies deserve a voice. Startups, independent researchers, open-source communities, universities, and affected users can all see risks and opportunities that major platforms may miss. A healthier AI ecosystem needs more than a conversation among giants.
AI breakthroughs need better public language
One reason the frontier AI debate feels confusing is that the language around it is often extreme. New systems are sometimes described as either world-changing miracles or immediate existential threats. Neither frame helps ordinary users, business leaders, or policymakers make grounded decisions.
Better public language would distinguish between capability, reliability, autonomy, access, and impact. A model can be highly capable in one domain and unreliable in another. A system can generate impressive text without being trustworthy enough for unsupervised decision-making. A tool can be safe in a narrow internal workflow and risky when released broadly.
Clearer language also helps people understand what AI breakthroughs actually mean. A breakthrough may be a visible new capability, but it may also be a quieter improvement in safety testing, efficiency, reasoning consistency, privacy, or user control. Not every important advance looks dramatic in a demo.
If industry giants want public trust, they need to communicate in ways that invite understanding rather than awe. If critics want accountability, they need to describe risks precisely rather than relying only on alarm. Better language will not solve the governance challenge, but it can make the debate more honest.
Practical principles for responsible frontier AI progress
The future of frontier AI will not be shaped by one decision. It will be shaped by thousands of choices about research priorities, release timing, access levels, safety investment, product design, and accountability. The following principles can help keep the conversation grounded:
- Match oversight to capability. More powerful systems deserve more rigorous testing, monitoring, and governance.
- Separate research from release. Discovering a capability does not mean it must be deployed immediately or broadly.
- Treat safety as engineering work. Responsible AI requires tools, processes, metrics, and ownership, not just values statements.
- Preserve room for competition. Rules should reduce harm without automatically entrenching the largest players.
- Invest in evaluation. Better tests help everyone understand what models can and cannot do.
- Keep humans accountable. AI systems may assist decisions, but organizations remain responsible for how they are used.
- Update policies as systems evolve. Governance should learn from incidents, research, and real-world deployment.
These principles are not a complete solution, but they point toward a healthier balance. They allow AI development to continue while making it harder to ignore warning signs.
The future will favor trusted innovation
The debate over slowing frontier AI is really a debate over what kind of progress the industry wants. Pure speed can produce impressive moments, but trust is what turns powerful technology into lasting infrastructure. If users, businesses, and governments do not trust how systems are built and deployed, even strong capabilities can face resistance.
Industry giants have a major role to play because they control resources, platforms, talent, and distribution. But they should not be the only voices defining the future. The direction of frontier AI should include researchers, smaller companies, policymakers, workers, educators, creators, and communities affected by deployment.
The best outcome is not a frozen field or an unchecked race. It is an AI ecosystem where breakthroughs continue, safety improves, and adoption becomes more thoughtful. Frontier AI will keep advancing, but the winners may be the organizations that prove they can innovate with restraint, clarity, and responsibility.
For anyone watching the next wave of AI research trends, the signal to follow is not just who builds the most powerful model. Watch who builds the most trustworthy path from research to real-world use.